October 10, 2026
Cloudflare has detailed a multi-agent security-operations harness built to assemble and verify evidence before an AI system recommends how analysts should handle an alert.
The company says its first prototype gave one general-purpose agent an entire investigation. That approach produced useful analysis but also created three recurring problems: contextual information could be mistaken for proof, the investigation’s scope could drift, and a failed lookup could become indistinguishable from a search that found nothing.
Reconnaissance before model analysis
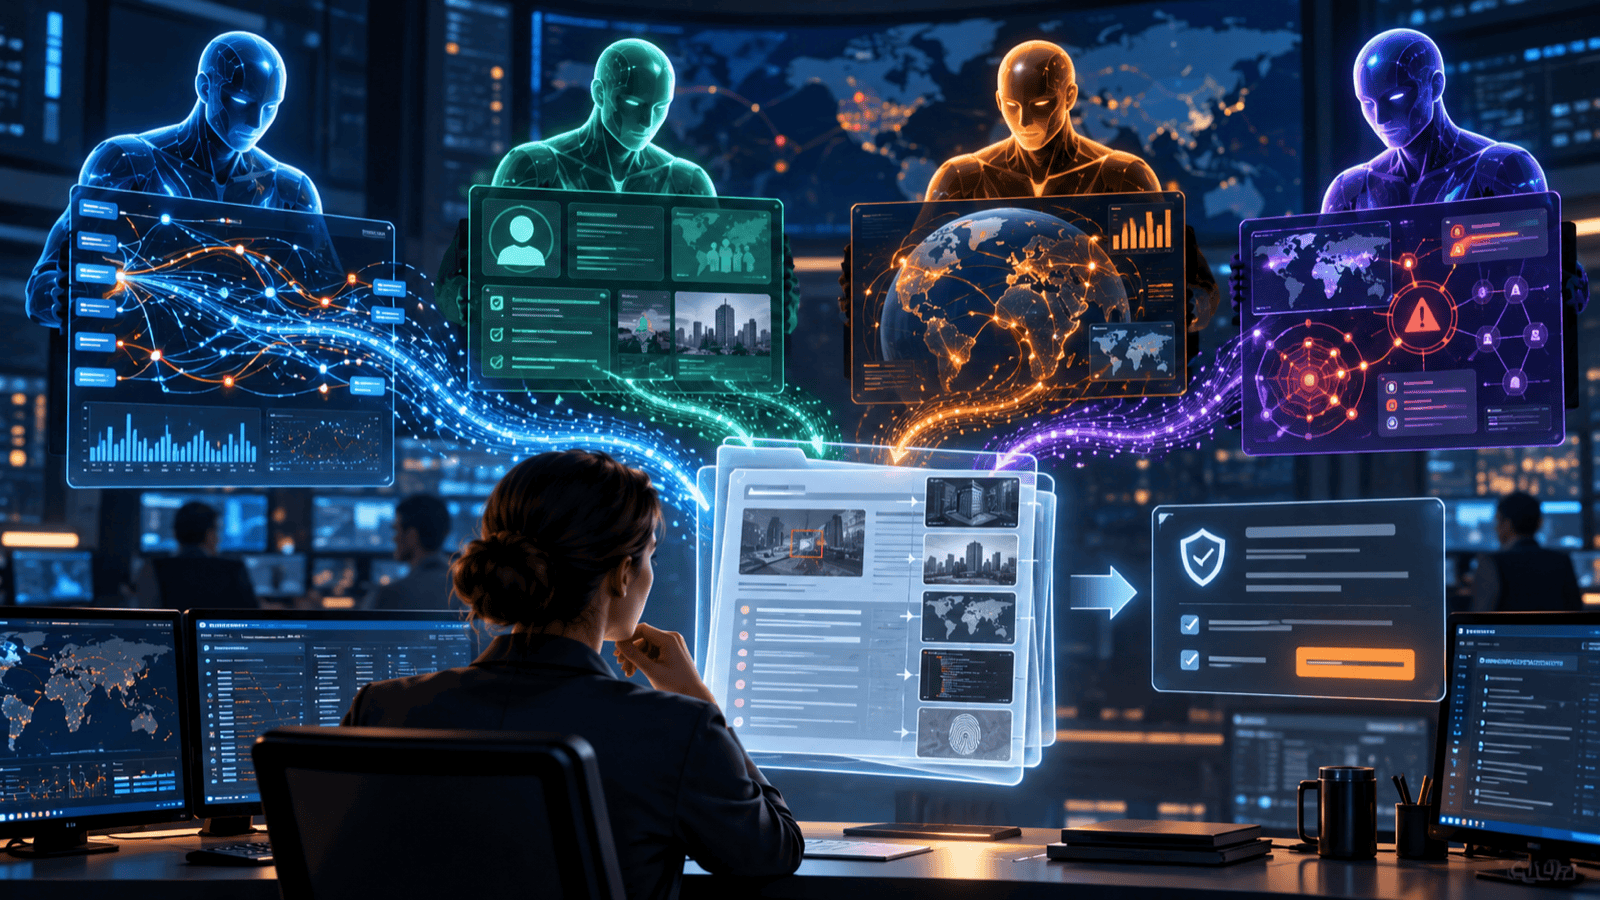
Cloudflare’s revised workflow begins with deterministic application code rather than an AI agent. Fixed reconnaissance jobs collect the customer identity, detection history, traffic baseline, enforcement outcome and network observations. Each item is stored with its source, version and timestamp so the same evidence snapshot can be replayed.
Alerts that need deeper review are then divided among four specialist agents covering traffic analysis, customer context, privacy-preserving global telemetry and threat intelligence. A synthesis agent combines their typed findings but cannot fetch new evidence or choose a classification outside an approved vocabulary.
Application code checks that citations exist, belong to the investigation and support the associated claim. Related alerts are grouped into cases, with evidence gaps and uncertainty preserved instead of being hidden behind confident prose.
Cloudflare says a Managed Defense analyst remains responsible for the final judgment and any mitigation. The automated system handles repetitive collection and correlation work, while the human reviewer can accept or revise the recommendation with the underlying evidence visible.
The design is a practical response to a core problem in AI-assisted security: fast analysis is only useful when investigators can see what the system knows, what it did not check and why it reached its conclusion.
Source: Cloudflare’s technical overview.